R&S®Trusted VPN
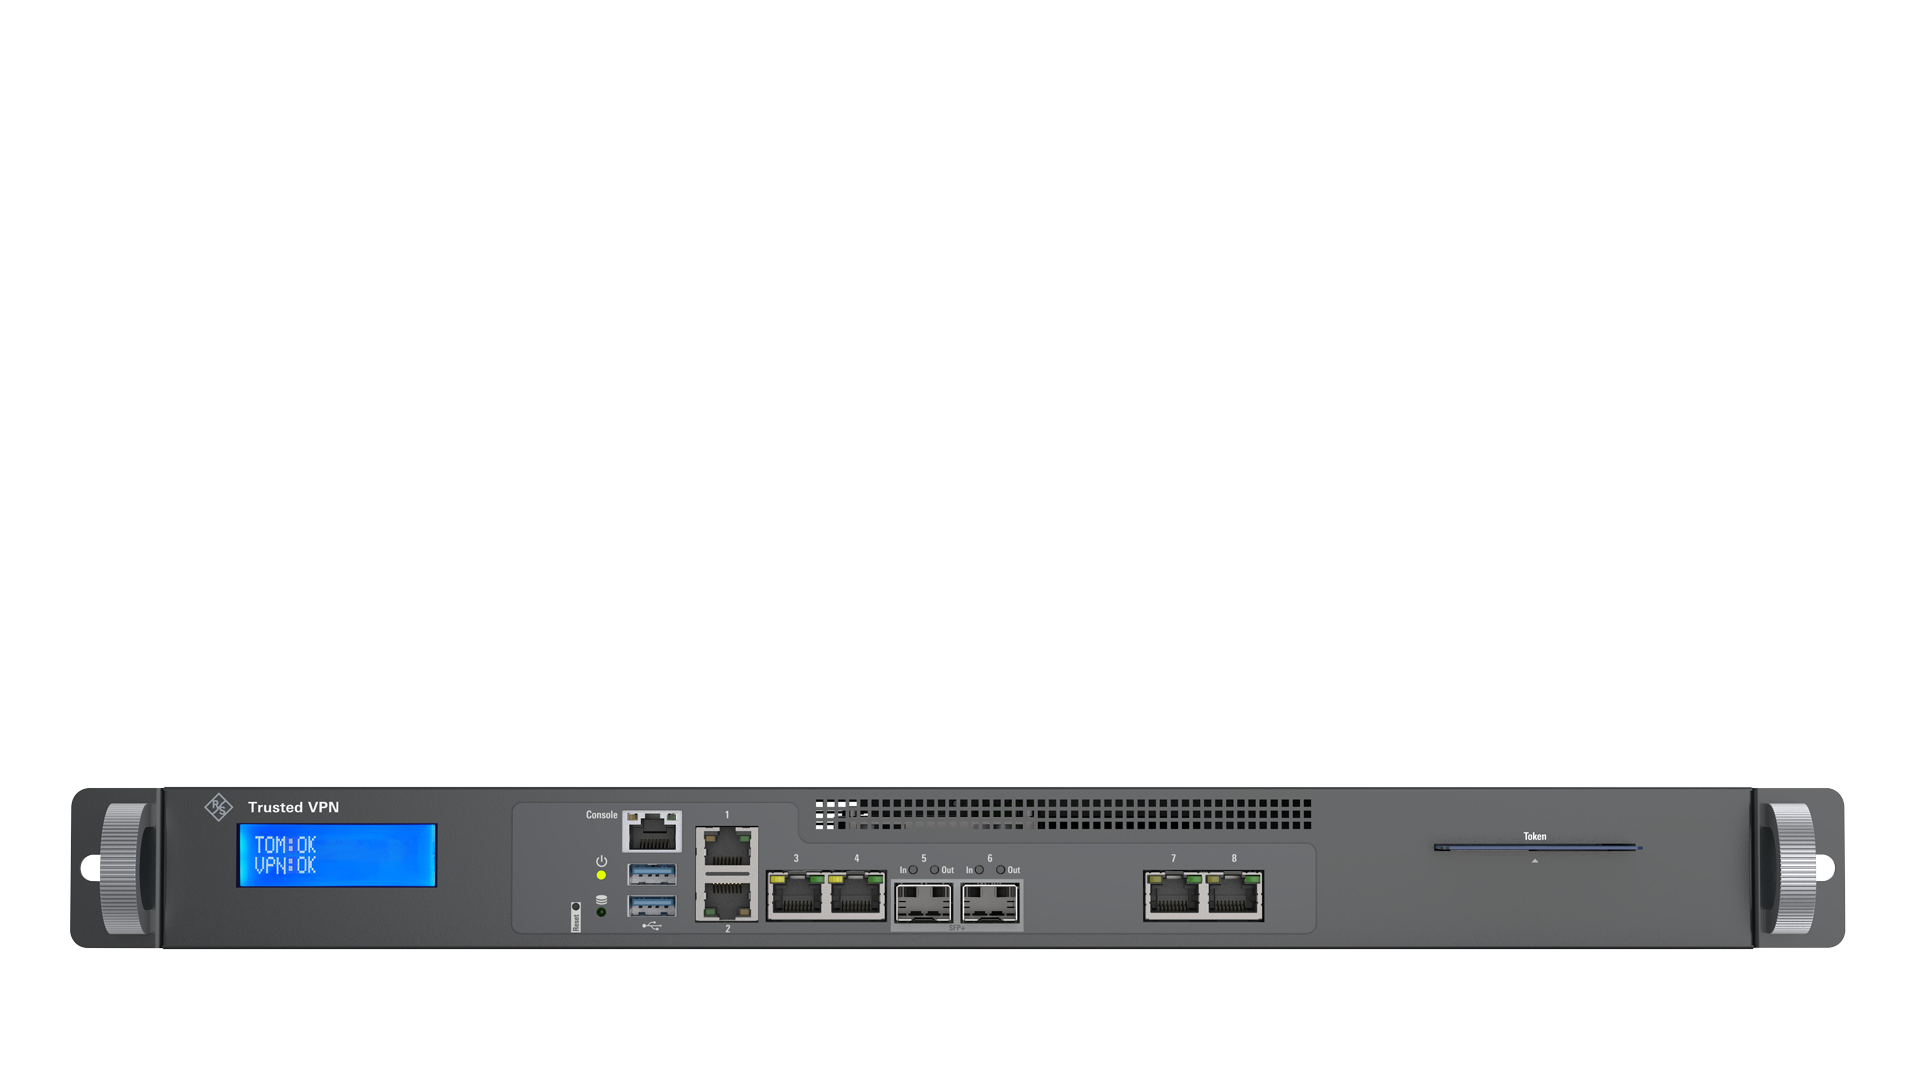
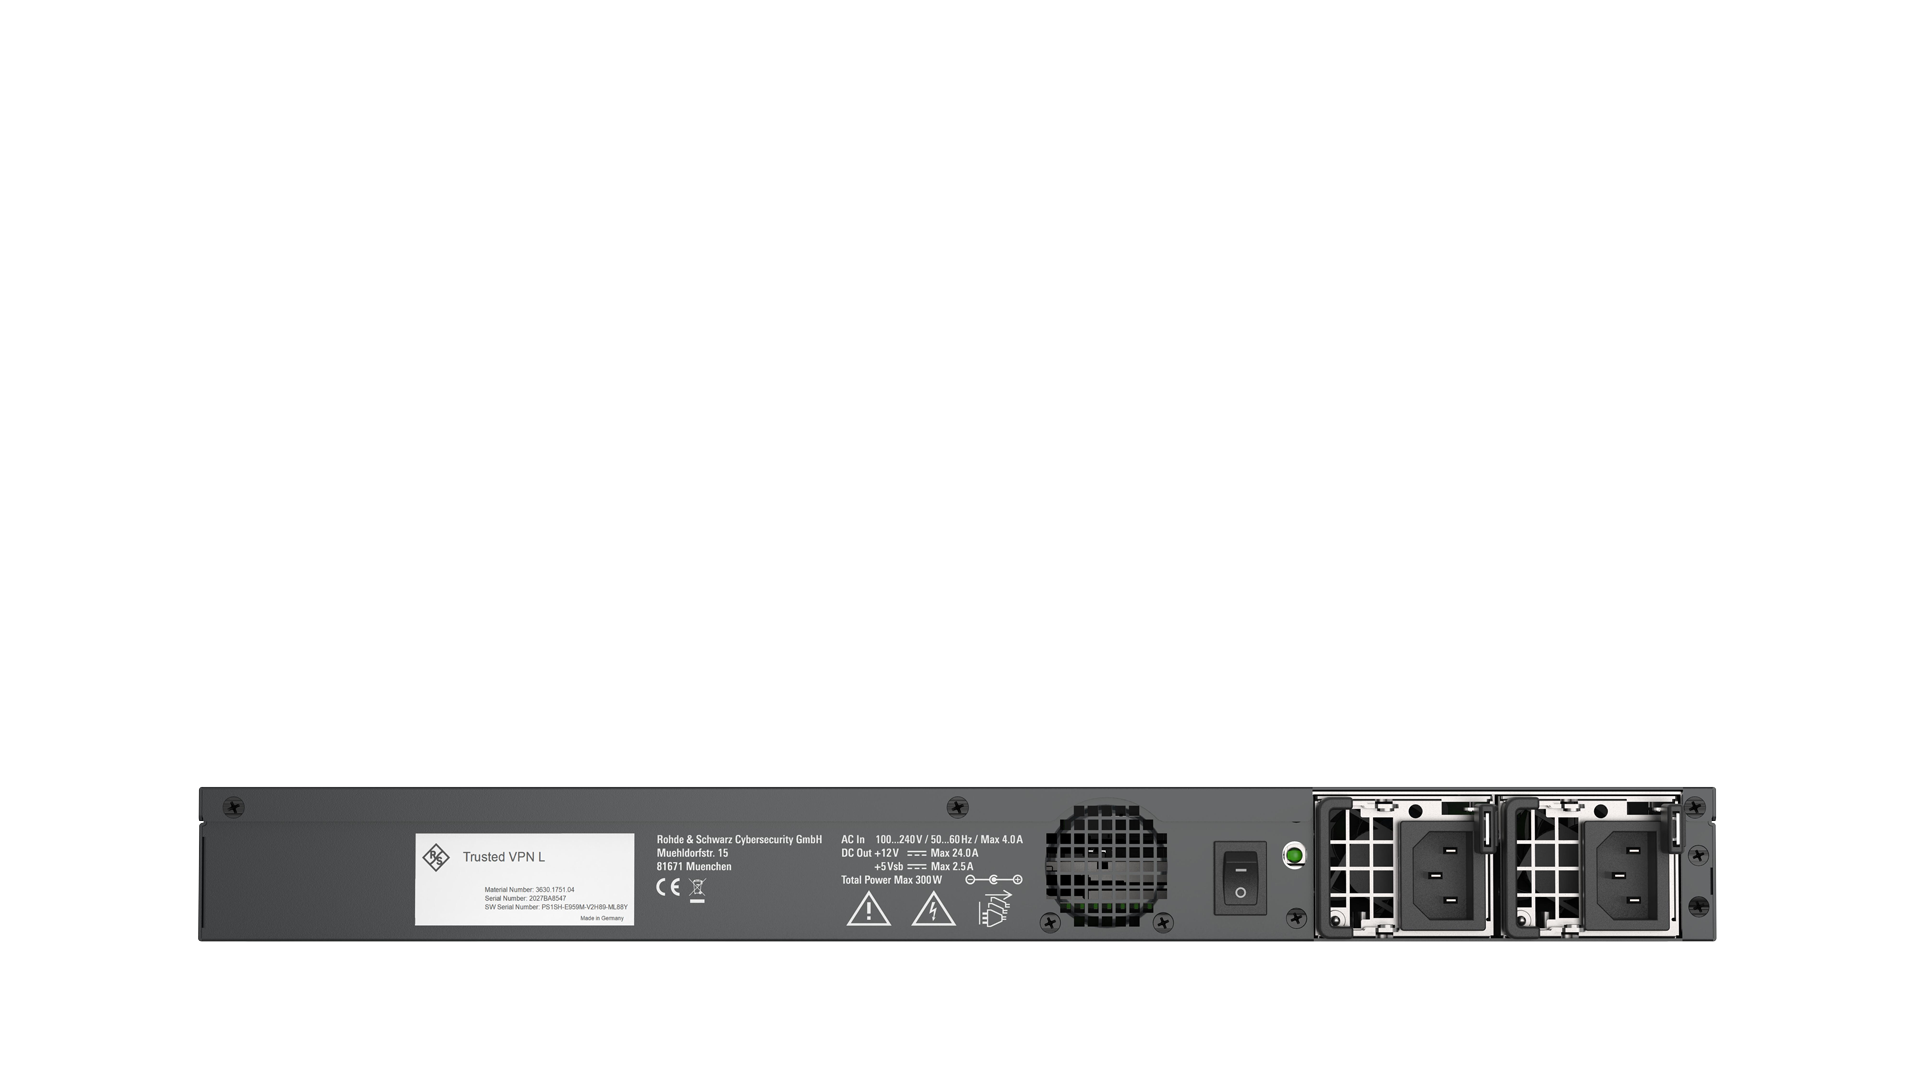
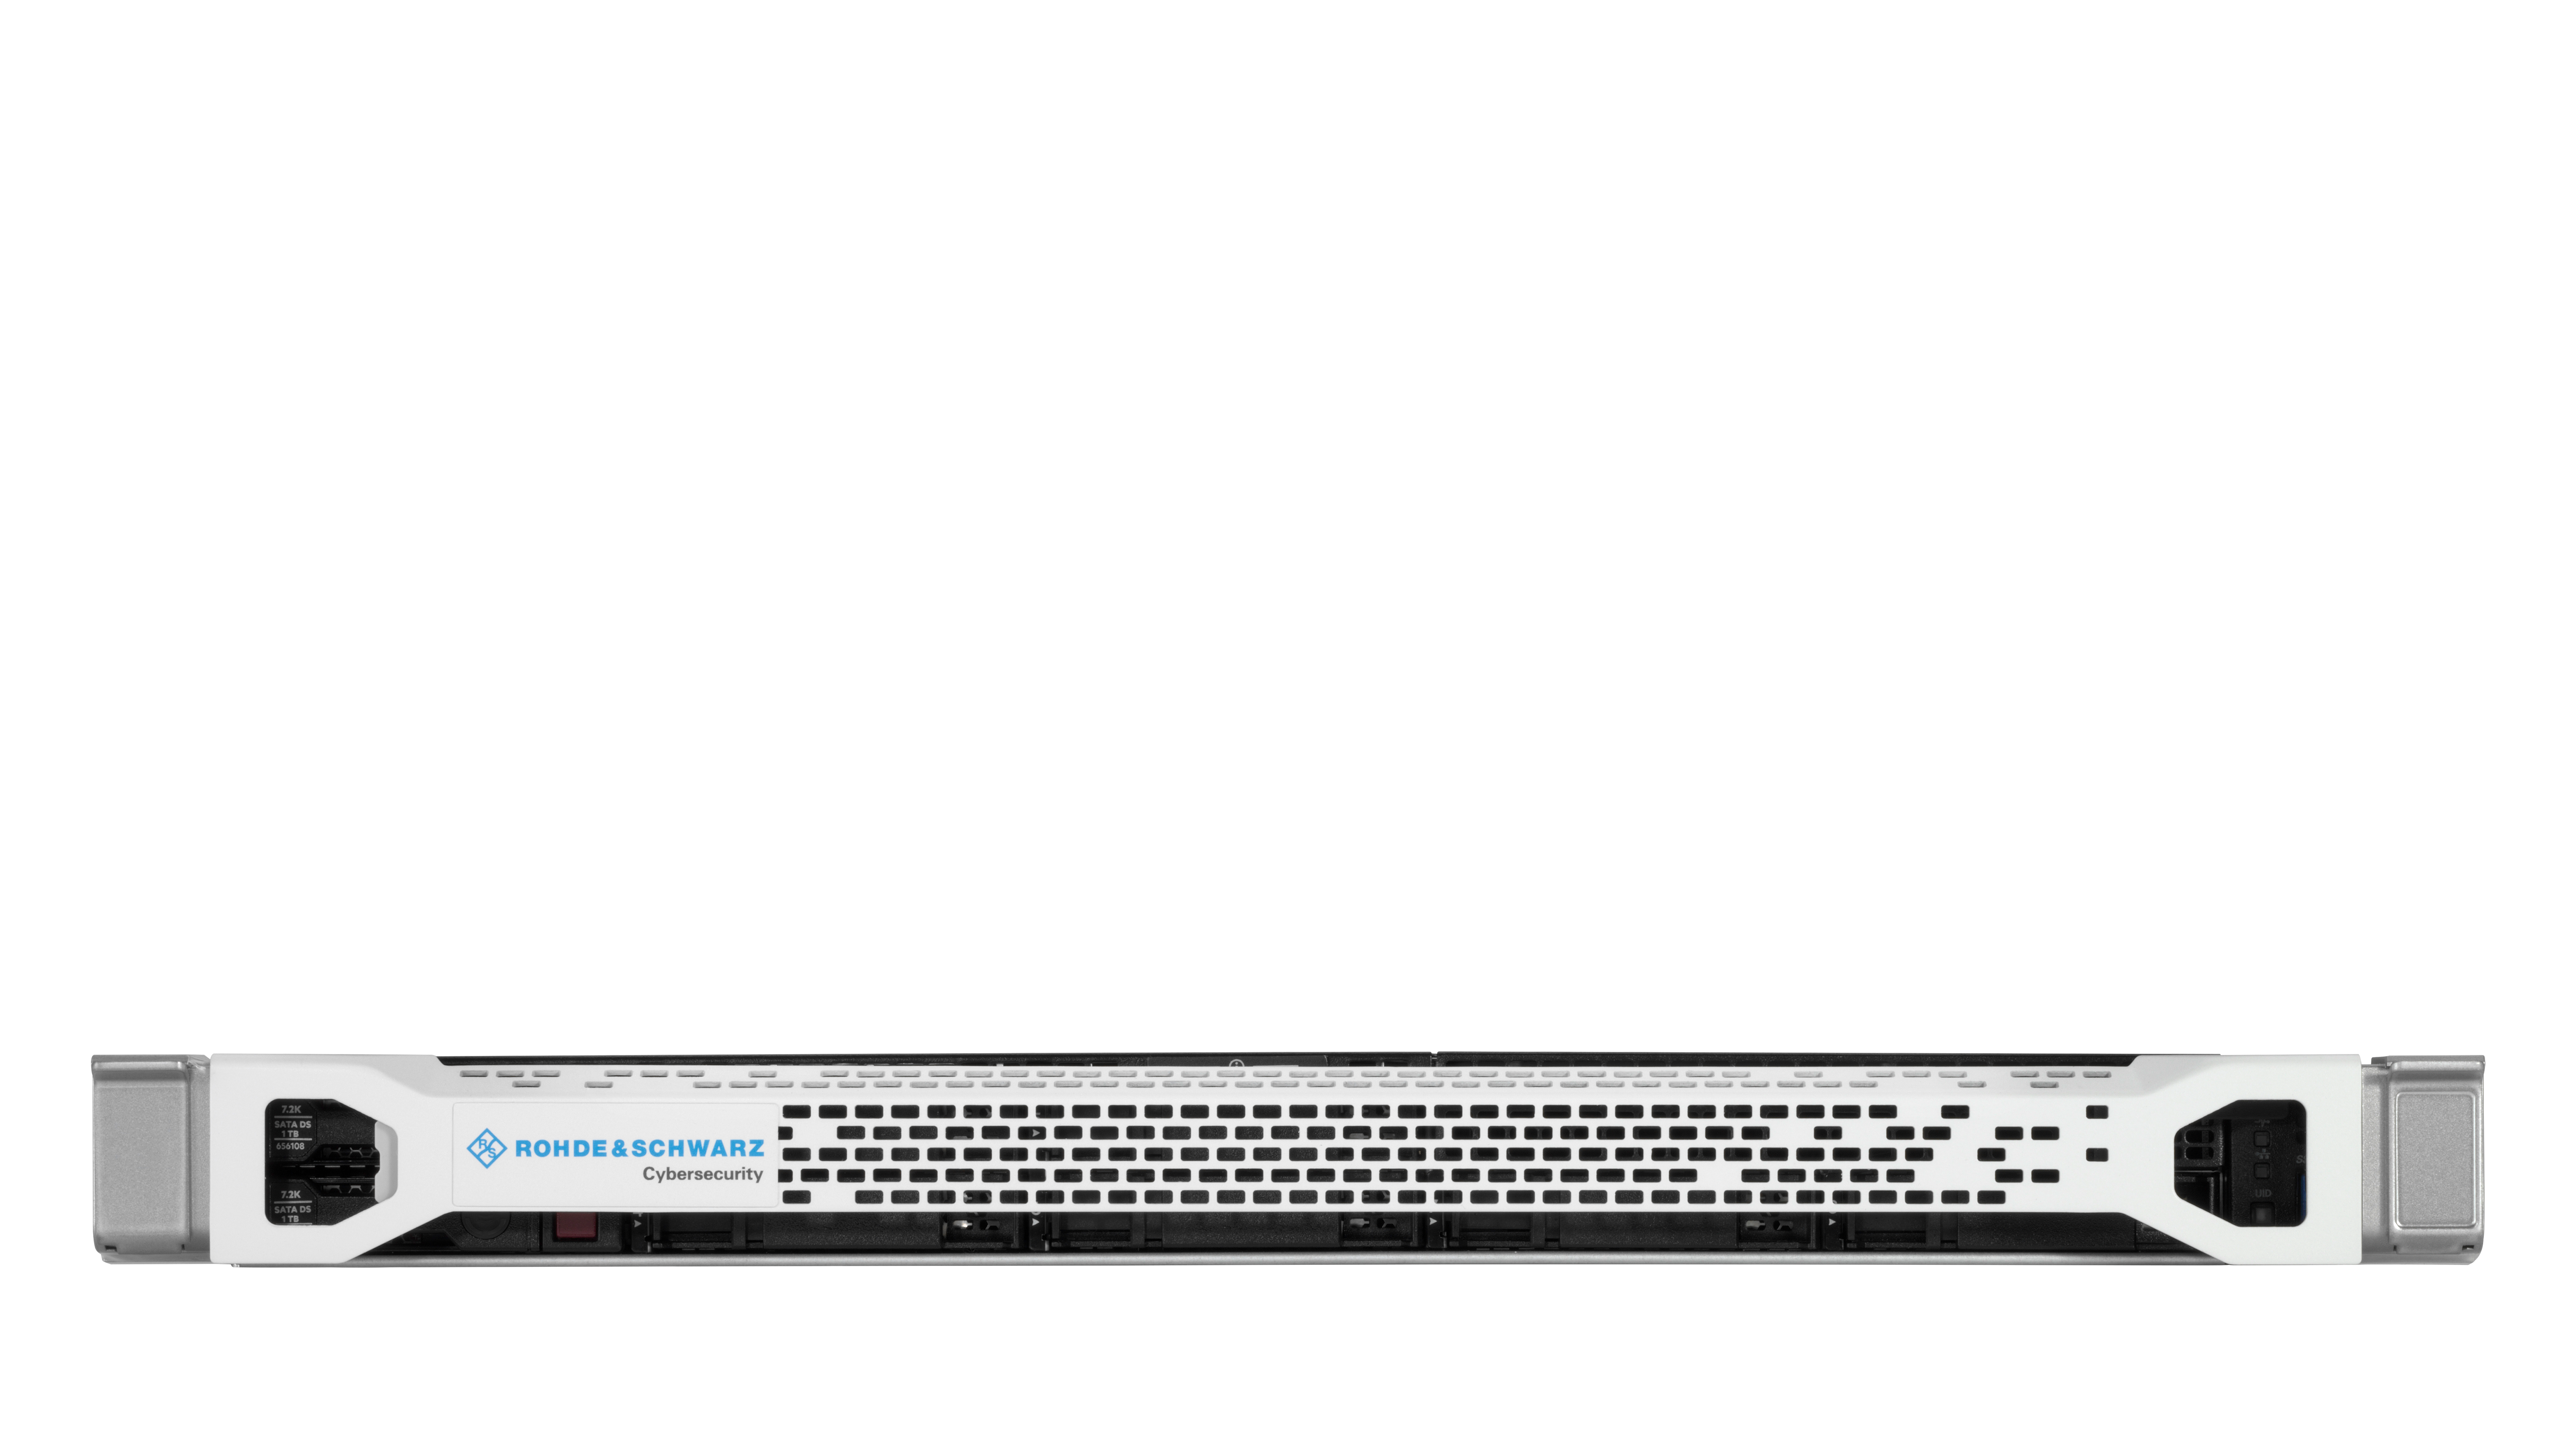
Layer 3 encryption approved by the German Federal Office for Information Security (BSI)
Protect classified information as it travels between your sites: R&S®Trusted VPN provides Layer 3 encryption approved by the German Federal Office for Information Security (BSI) for VS-NfD, EU RESTRICTED, and NATO RESTRICTED. Public authorities and companies can use it to secure their IP communications over public and managed networks. IPSec, cryptographic network separation, and hardware-based system protection work together to provide comprehensive security. With the R&S®Trusted Objects Manager, you can centrally manage gateways and keys – tailored to your security requirements.
- Approval by the German Federal Office for Information Security (BSI) for the transmission of information classified as VS-NfD, EU RESTRICTED, and NATO RESTRICTED
- Layer 3 encryption with IPSec for site-to-site and client-to-site connections
- Use over public IP networks and managed IP services such as MPLS
- Trusted Virtual Domains for cryptographic separation of communication domains
- Integrated certification authority; external CA for road warrior connections
- UEFI Secure Boot, TPM-based Trusted Boot, and disk encryption
- Centralized management via R&S®Trusted Objects Manager with web-based operation and integrated automated PKI
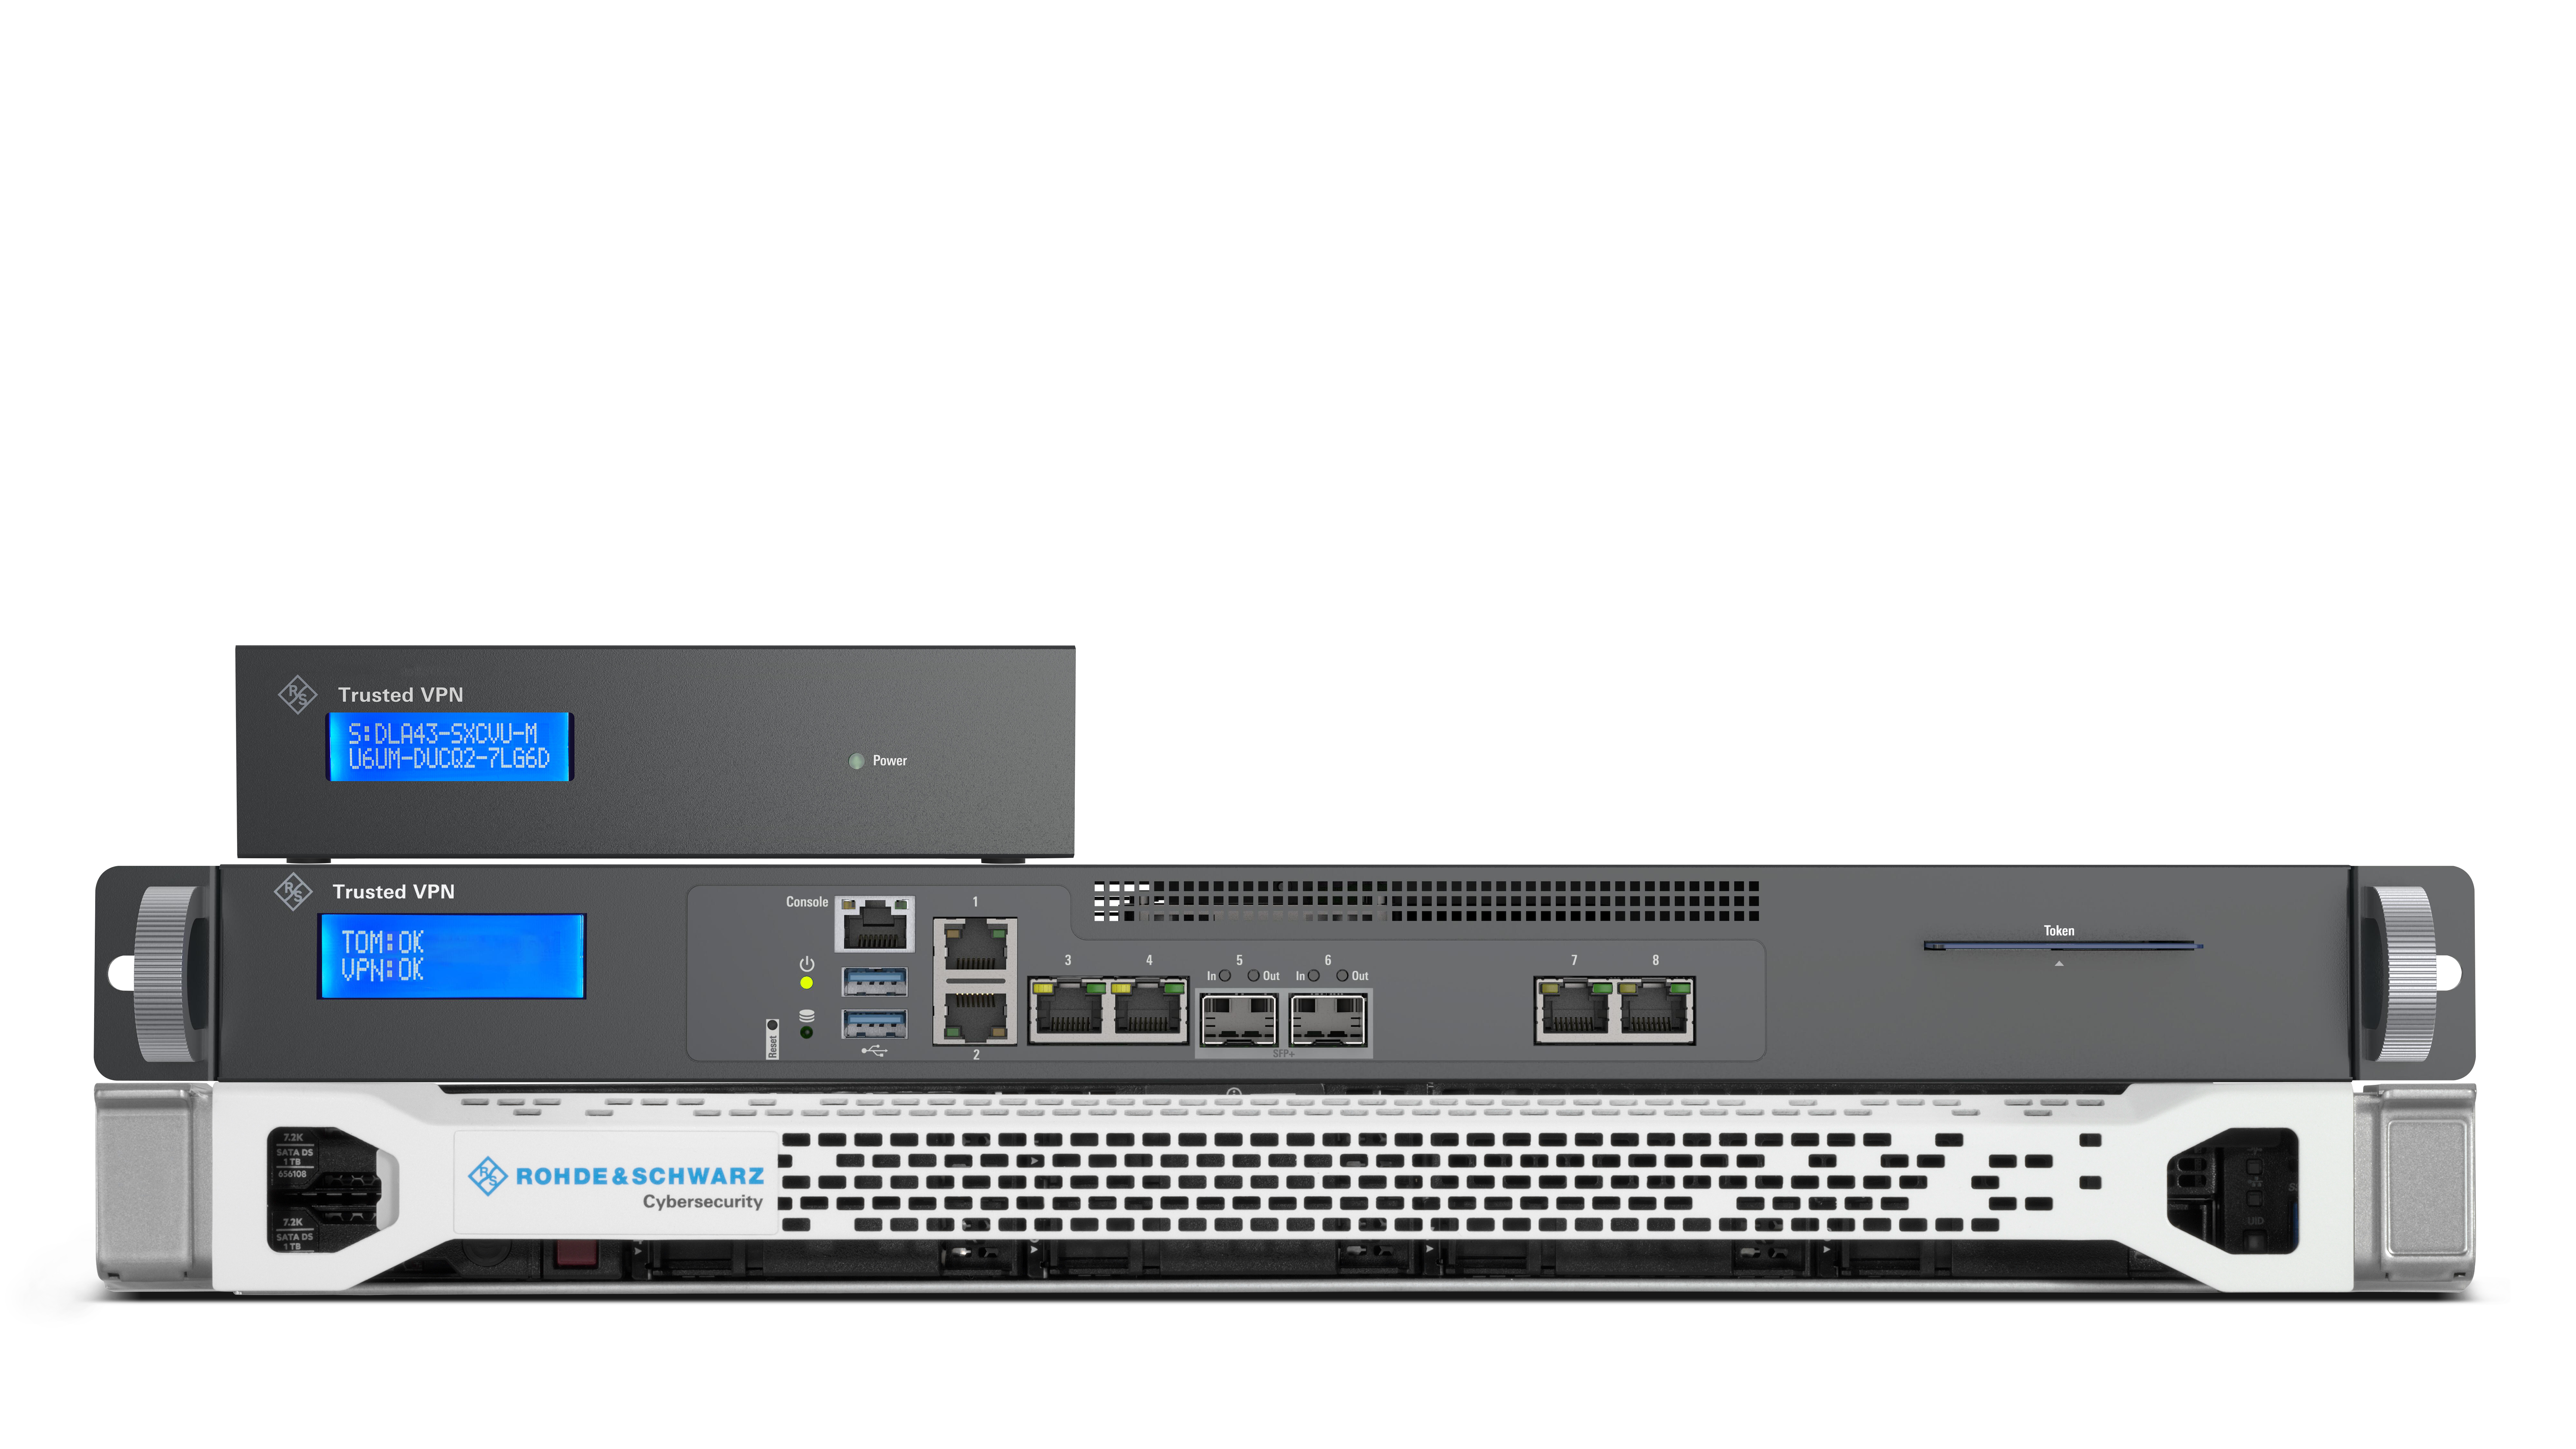
- Three models that can be combined: VPN-S with up to 250 Mbps, VPN-L with up to 600 Mbps, and VPN-XL with up to 6 Gbps of bidirectional encryption performance
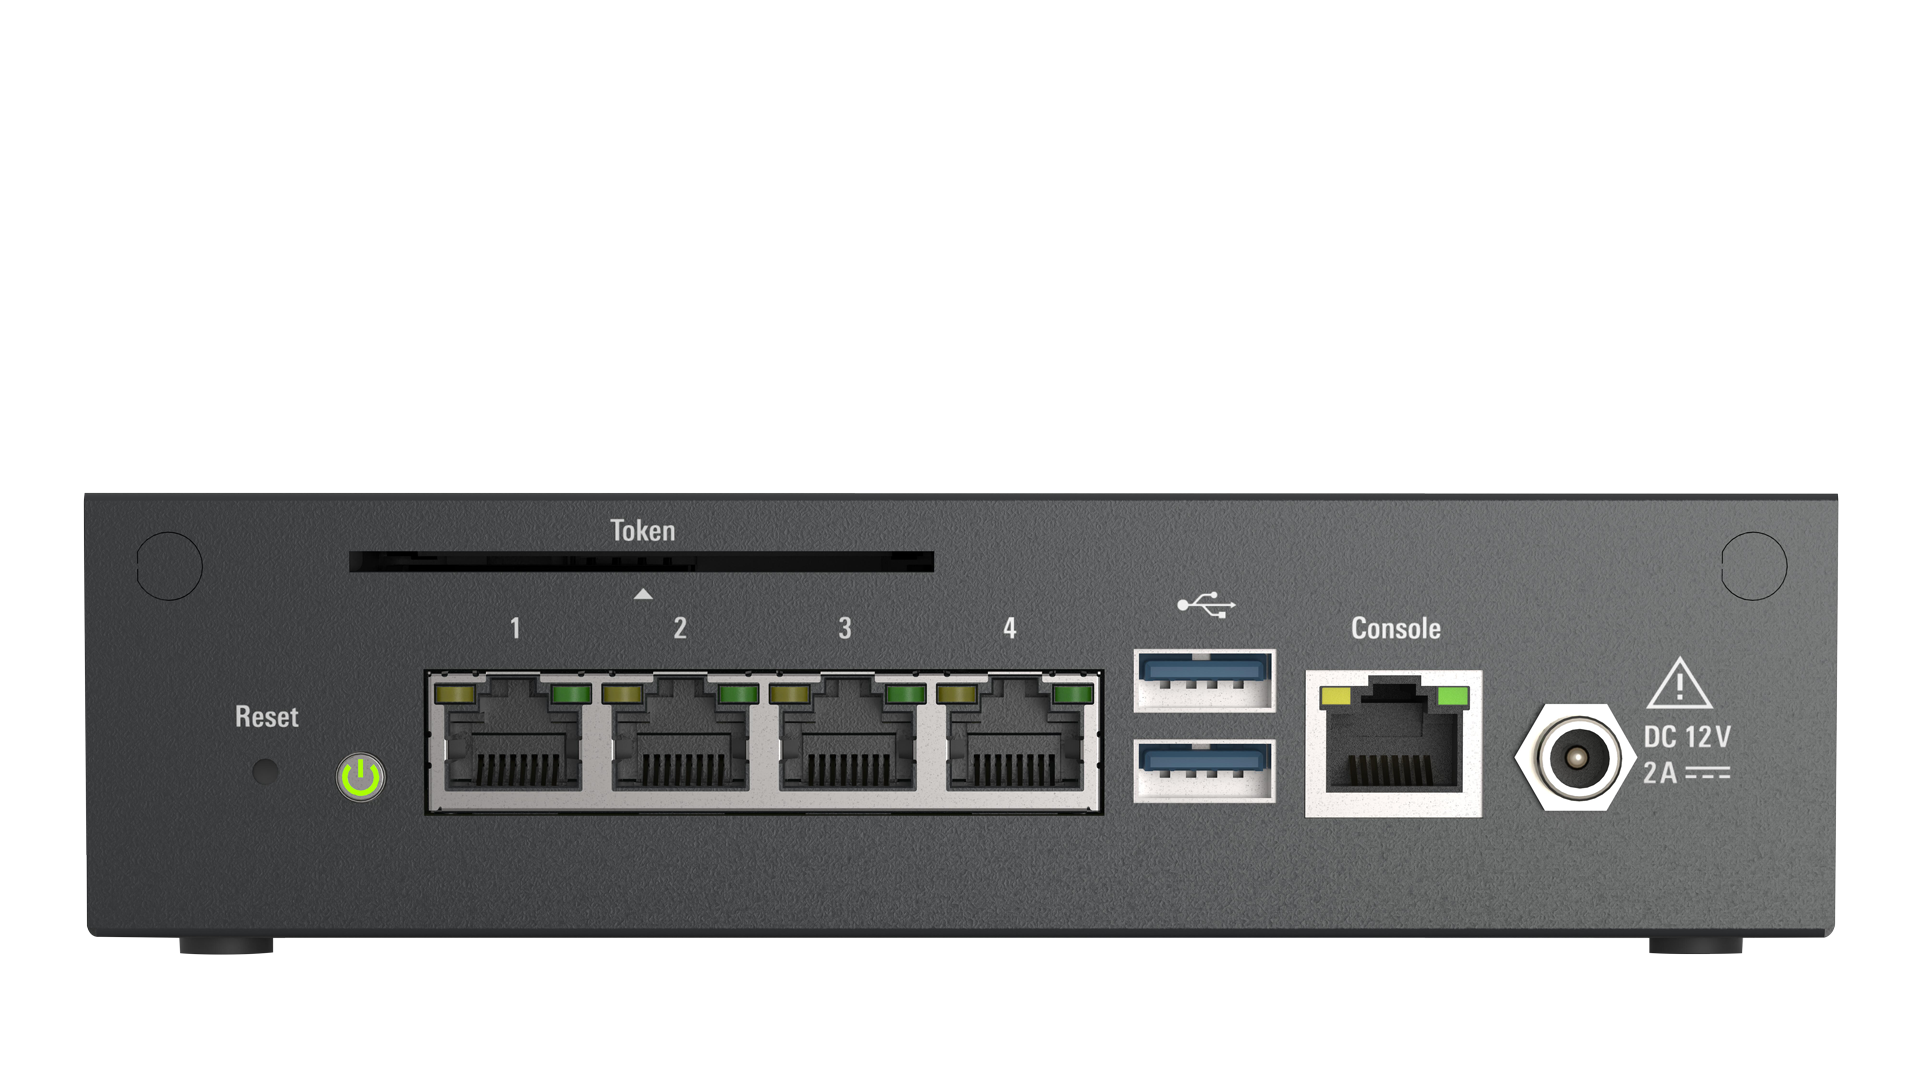
- Gigabit Ethernet interfaces on all models; additional 10 Gigabit Ethernet SFP+ interfaces on VPN-L and VPN-XL
Approved security for classified information
When public authorities and their contractors exchange classified information, the required level of protection must also be maintained during transmission. R&S®Trusted VPN provides encryption approved by the German Federal Office for Information Security (BSI) for VS-NfD, EU RESTRICTED, and NATO RESTRICTED. This enables you to secure site-to-site communications for public institutions as well as companies and project partners that transmit information classified at these levels. This approval is a key selection criterion for these security-critical applications.
Centralized control of gateways and keys
Maintain a clear overview even in distributed VPN infrastructures: With the R&S®Trusted Objects Manager, you can centrally manage gateways, certificates, and trust relationships between sites, networks, and users. The web-based interface and integrated automated PKI simplify administration. This allows you to consolidate the security management of your sites in one central location.
Cryptographic separation for different security domains
Shared infrastructure places specific demands on the separation of sensitive communications. Trusted Virtual Domains enable you to cryptographically isolate organizational units, projects, or security zones from one another. The respective trust relationships are managed centrally. This allows you to operate separate communication domains on a shared infrastructure and maintain a clear overview of their assignment even as additional sites are added.
Secure site networking over public and managed networks
Whether via the Internet or a managed IP service such as MPLS, R&S®Trusted VPN protects your site communications regardless of the transport network used. The IPSec tunnels encrypt data and inner IP headers, concealing internal addressing from the transport network. This enables public authorities,…
Flexible connectivity for sites and mobile workplaces
Connect branch offices to your headquarters and enable secure access to corporate resources while on the move or working from home. R&S®Trusted VPN supports site-to-site and client-to-site connections within a common management and security architecture. NAT traversal enables deployment behind NAT…
Strong cryptography for trusted connections
AES-256-GCM protects the confidentiality and integrity of your transmitted data. To establish trusted VPN connections, R&S®Trusted VPN combines authentication using X.509 certificates with the IKEv2 key exchange protocol. Perfect Forward Secrecy protects previous sessions even if long-term keys are…
Integrated system protection from startup
Protection of your VPN infrastructure begins as soon as the system starts: UEFI Secure Boot and TPM-based Trusted Boot safeguard the integrity of the system software. Disk encryption protects stored data against unauthorized access. This means that the security concept covers not only transmitted…
Performance tailored to branch offices and central sites
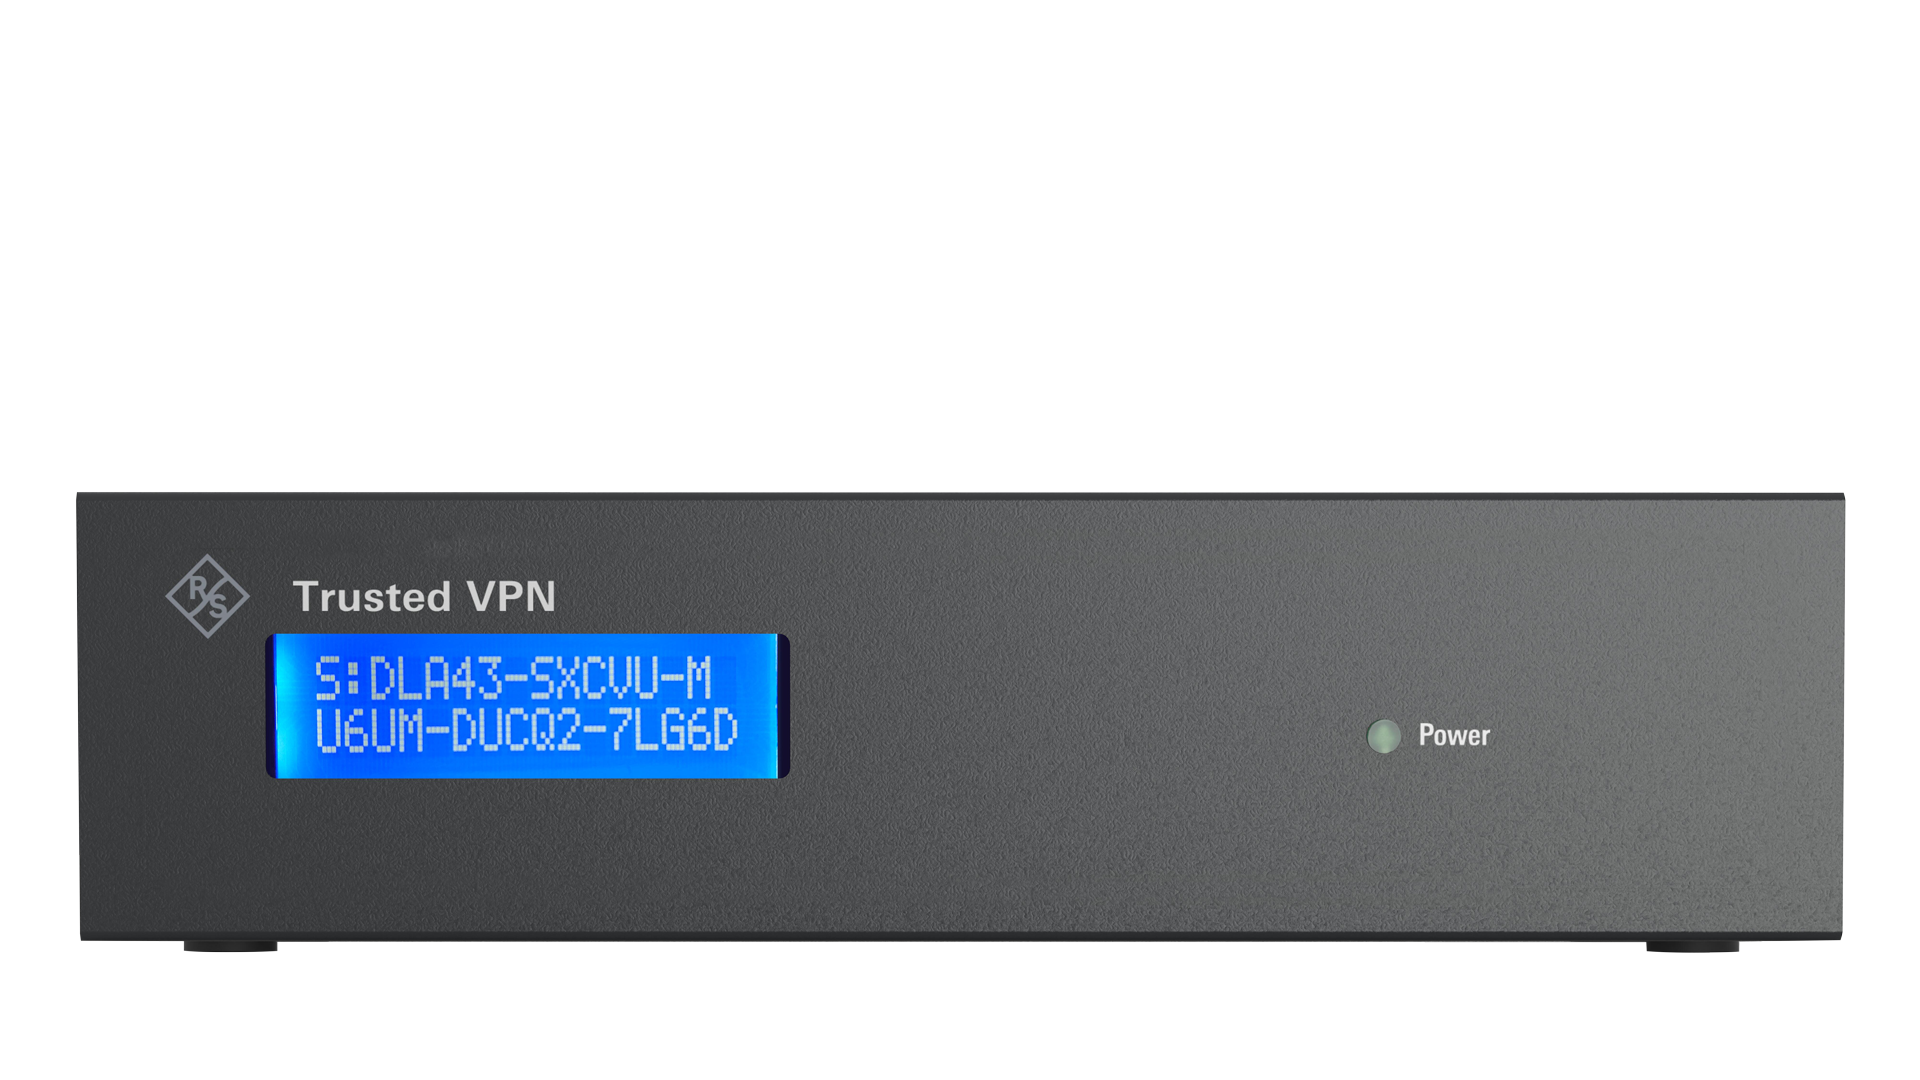
Configure your VPN infrastructure to meet the specific requirements of each site: The S, L, and XL models can be operated together. VPN-S offers a compact, passively cooled desktop format for smaller sites. VPN-L combines a 19-inch format with Gigabit and 10 Gigabit interfaces. For central sites…