R&S®Trusted Objects Manager
Centralized management system for the R&S endpoint and network encryption portfolio
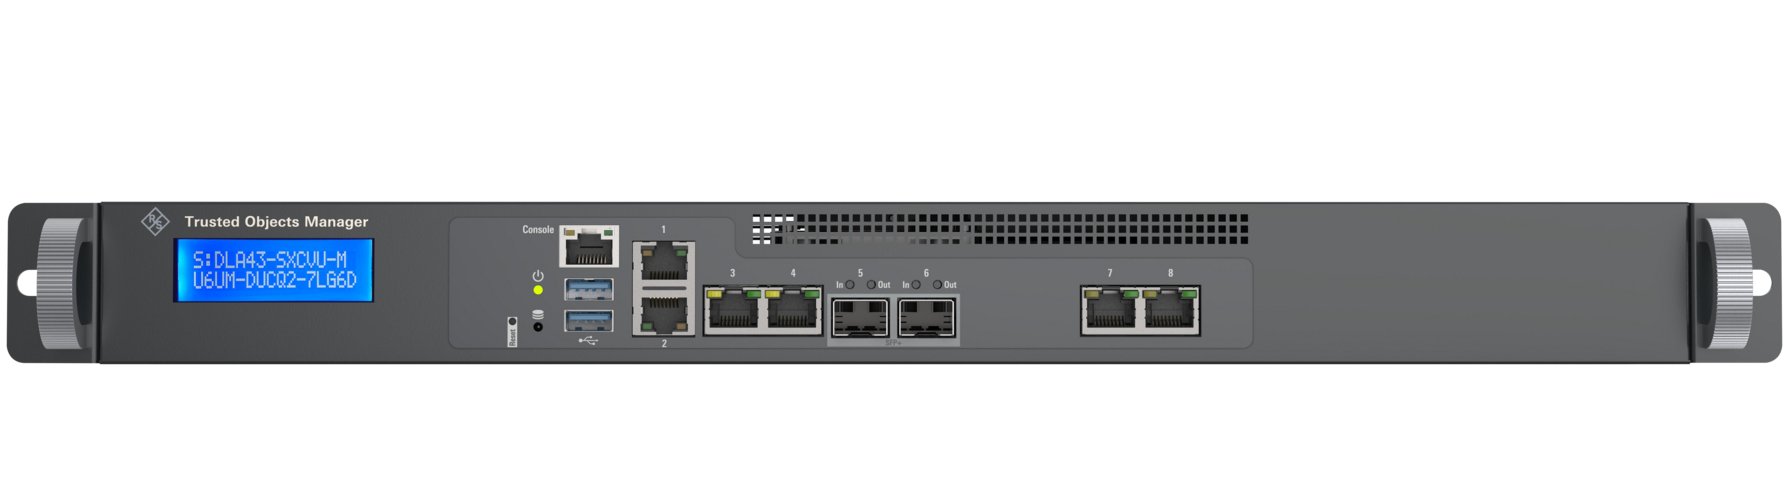
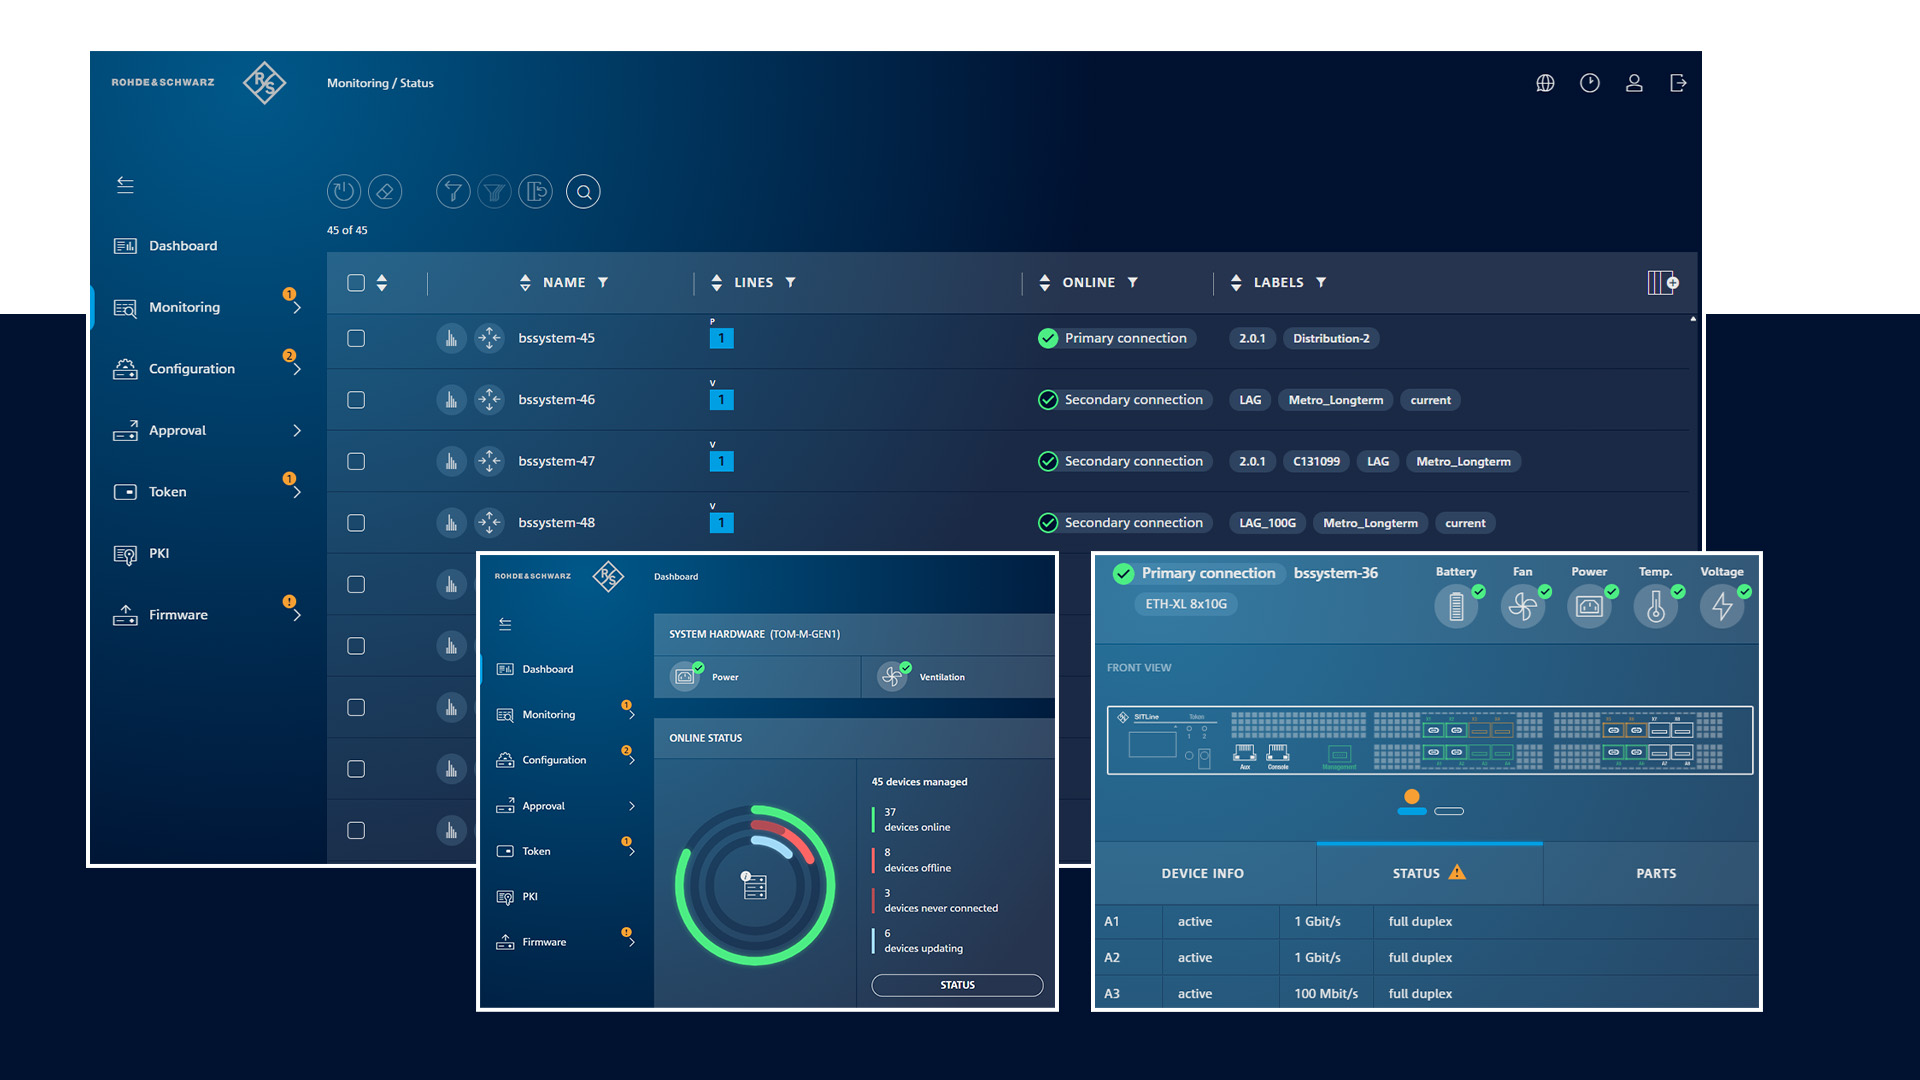
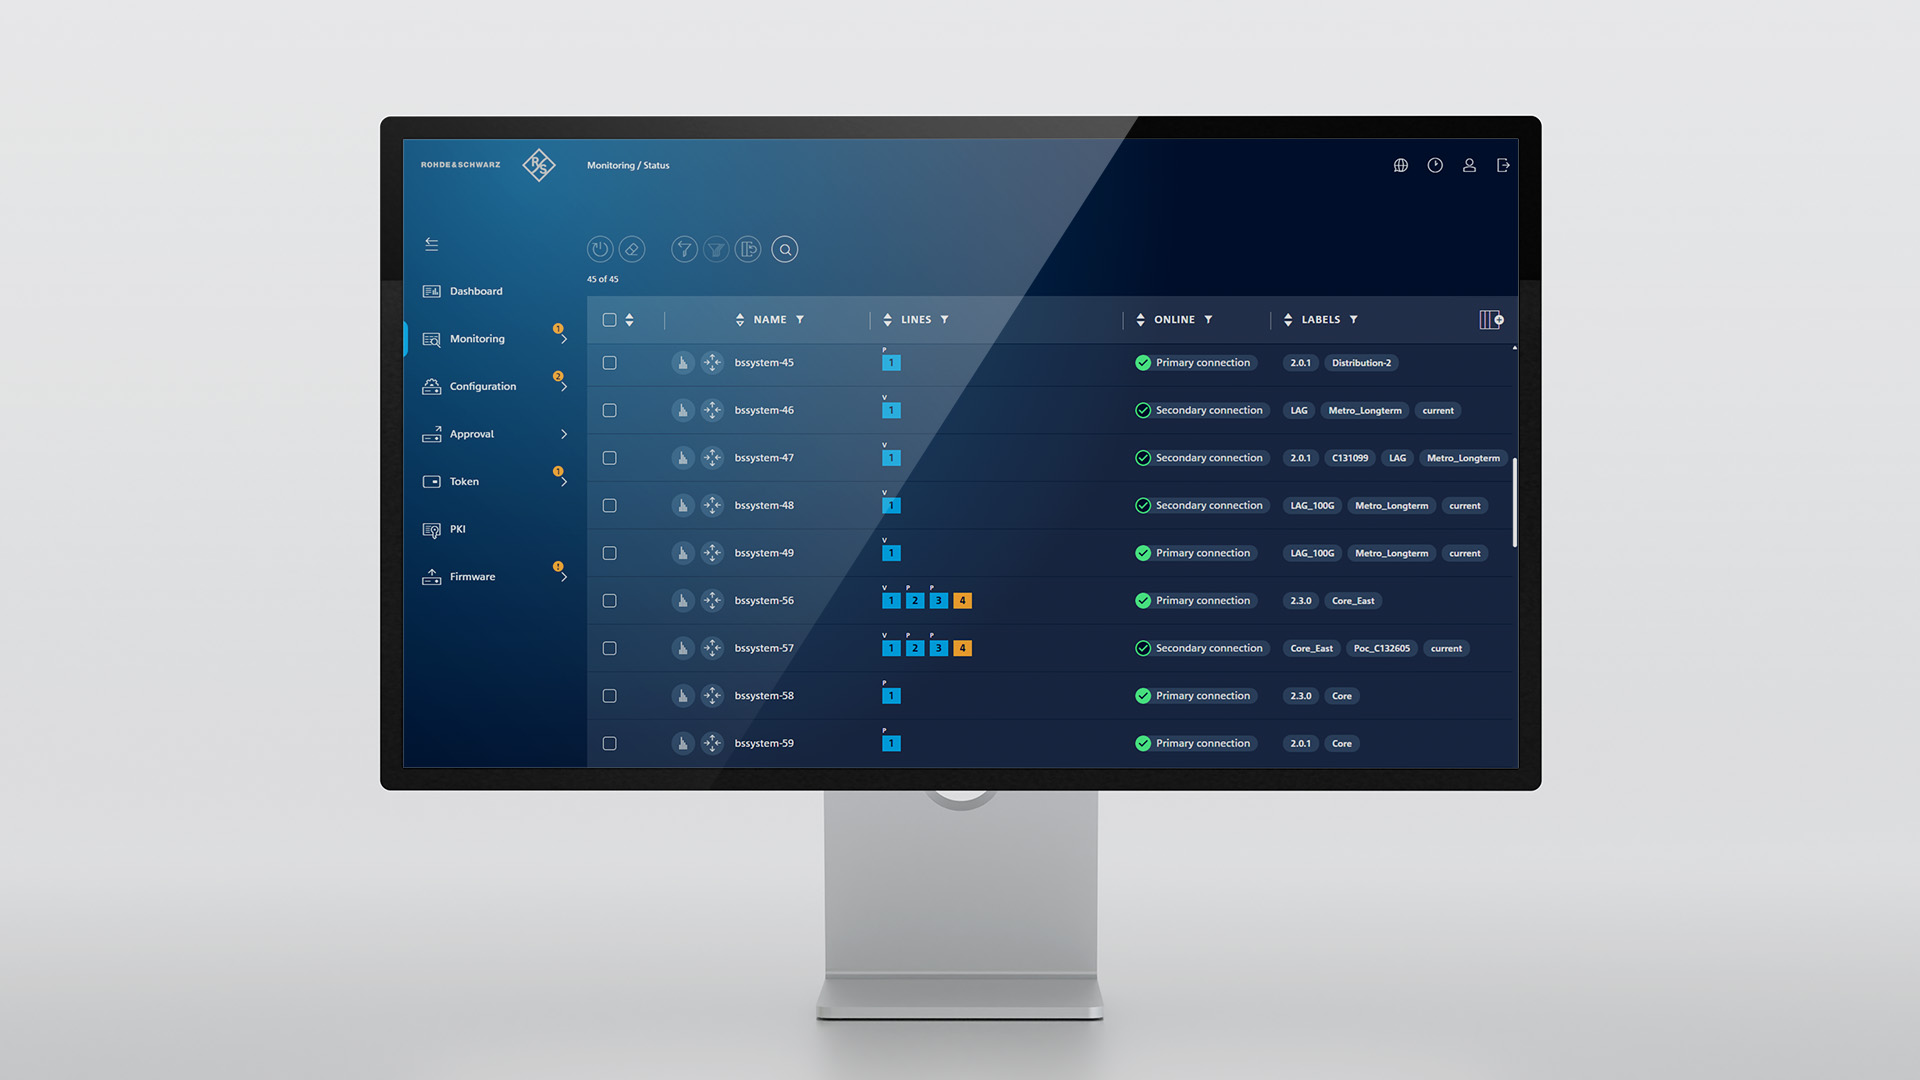
The more endpoints, users, and locations an organization has, the more important reliable, comprehensive management becomes. The R&S®Trusted Objects Manager (TOM) is the central management appliance for the R&S endpoint and network encryption portfolio (including R&S®Trusted Disk, R&S®Trusted VPN, and R&S®SITLine). Deployed within the organization's own infrastructure, it ensures that management of R&S products remains entirely under the organization's control. Through a secure, intuitive web interface, administrators can manage R&S products, including users, permissions, and smart cards, while closely monitoring the operation of the managed systems. The integrated public key infrastructure (PKI) also enables independent, centralized management of keys and certificates under the organization's own control.
- Hardware appliance serving as a central management system for managing devices in the R&S endpoint and network encryption portfolio (including R&S®Trusted Disk, R&S®Trusted VPN, and R&S®SITLine)
- Administration via a secure web interface designed for ease of use and intuitive operation
- Integrated public key infrastructure (PKI) that can be operated independently without third-party involvement
- Centralized, intuitive user and permissions management
- Scriptable API
- Integration with LDAP directory services, including Microsoft Active Directory and OpenLDAP
- Support for importing users and user groups from existing LDAP structures
- Support for deploying additional TOM instances as standby instances
- Two hardware variants available: TOM-S and TOM-M (both as 19-inch rack-mounted appliances)
- Secure management environment for R&S products approved for use up to VS-NfD, RESTREINT UE/EU RESTRICTED, and NATO RESTRICTED classification levels
Simple, clear, and efficient security management
The R&S®Trusted Objects Manager consolidates administrative tasks for the R&S endpoint and network encryption portfolio in a centralized, user-friendly management interface. Through the secure web interface, administrators can set up and configure devices, manage users and permissions, implement security policies, deploy updates, and monitor ongoing operations. Designed around typical user workflows, the intuitive interface ensures clear processes and reduces administrative effort, even in complex security infrastructures.
Comprehensive control through deployment within your own infrastructure
The R&S®Trusted Objects Manager is provided as a ready-to-use hardware appliance, enabling fast and straightforward deployment of centralized security management. Operating within the organization's own IT infrastructure provides the foundation for maintaining independent control over security-critical systems and data. Companies and government agencies retain control over management, user, and certificate processes without relying on external cloud or third-party providers. Different hardware variants are available to meet specific requirements.
Integrated PKI for independent certificate management
With its integrated public key infrastructure management capabilities, the R&S®Trusted Objects Manager provides a centralized foundation for securely managing digital identities and certificates. The PKI operates entirely under the organization's own control, without relying on third-party providers. TOM can function as either a root or intermediate certificate authority or integrate into existing PKI structures. Centralized management of device and user certificates, based on established standards and protocols such as X.509, CRLs, OCSP, and ACME, along with configurable cryptographic algorithms, provides a flexible and trusted foundation for secure authentication and certificate management processes.
Seamless integration with existing user directories
Existing user structures can be integrated directly into centralized security management. Depending on the managed product, the R&S®Trusted Objects Manager supports integration with various LDAP directory services, such as Microsoft Active Directory and OpenLDAP. Users and user groups can be…
High availability through standby instances
Additional R&S®Trusted Objects Manager appliances can be connected as standby instances to ensure reliable, resilient operation. If the primary instance fails, a redundant management environment is available to increase the availability of centralized security management. Depending on the required…
For sensitive data and the highest security requirements
For information requiring special protection, TOM provides a management environment for R&S products approved for use up to VS-NfD, RESTREINT UE/EU RESTRICTED, and NATO RESTRICTED classification levels. This makes TOM suitable for use in security-critical environments within government agencies,…
Flexible integration via REST API
The integrated REST API allows the R&S®Trusted Objects Manager to be flexibly integrated into existing IT, monitoring, and reporting systems. Standardized interfaces enable automated retrieval of information and support centralized operational processes across multiple systems. This allows TOM to be…
|
R&S®Trusted Objects Manager S |
R&S®Trusted Objects Manager M |
|
|---|---|---|
|
Description |
Compact hardware appliance for small to medium-sized management environments |
High-performance hardware appliance for larger management environments and increased availability requirements |
|
Form factor |
19", 1U, depth: ~30 cm |
19", 1U, depth: ~74 cm |
The R&S®Trusted Objects Manager serves as the central management platform for R&S security solutions in the areas of network and disk encryption as well as VPN.

R&S®SITLine
The centralized and intuitive R&S®Trusted Objects Manager (TOM) gives administrators a clear overview of complex network topologies, security and certificate management, including tamper detection to ensure secure operation even without on-site monitoring.
More about R&S®SITLine

R&S®Trusted Disk
The R&S®Trusted Objects Manager enhances the R&S®Trusted Disk disk encryption solution by providing centralized management of endpoints, users, permissions, security policies, smart cards and certificates. It also supports operational monitoring, simplifying the administration of the entire disk encryption solution.
More about R&S®Trusted Disk

R&S®Trusted VPN
The R&S®Trusted Objects Manager also provides a centralized overview of distributed VPN infrastructures and enables consistent management of gateways, certificates and trust relationships between sites, networks and users. The web-based interface and integrated automated PKI simplify administration.
More about R&S®Trusted VPN